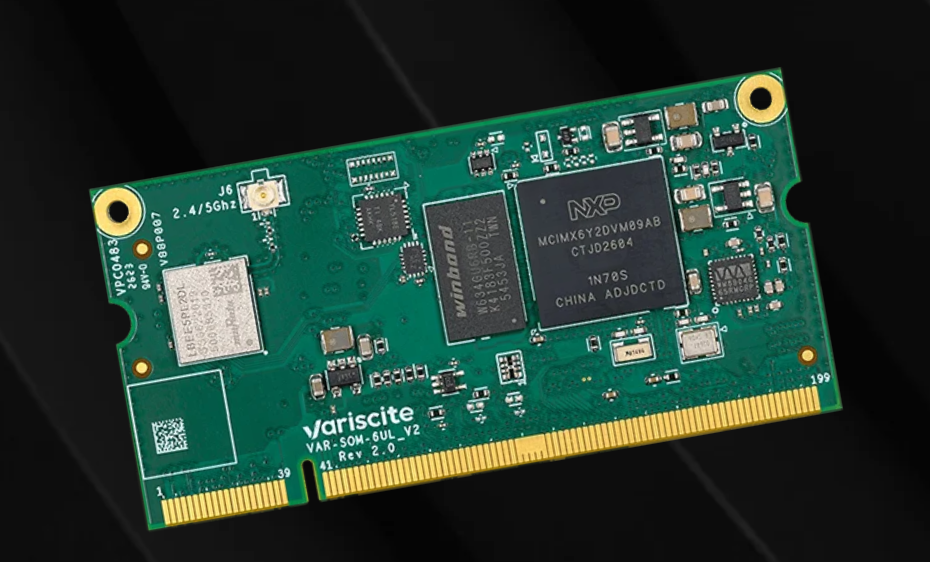
System on module (SoM) maker, Variscite, announces that its i.MX SoM portfolio of SoMs will be TPM 2.0 secure through the SecEdge SEC-TPM solution. The Trusted Computing Group’s TPM (Trusted Platform Module) 2.0 standard provides a protected environment for secure boot, device identity and the storage and use of cryptographic keys.
TPM 2.0 can be implemented as a discrete security chip or in firmware on the application processor. SecEdge’s SEC-TPM is a firmware implementation that runs in the OP-TEE secure world via Arm TrustZone. On i.MX 93 and i.MX 95 SoMs, it can leverage the processor’s security architecture, including the NXP EdgeLock Secure Enclave as the root of trust. Variscite customers can now add TPM 2.0 functionality using the processor already in the design.
“The future belongs to trusted devices. As regulatory requirements increase and cyber threats evolve, manufacturers need security that is both proven and practical. Our collaboration with Variscite brings hardware-anchored embedded TPM 2.0 security to millions of edge devices using the silicon already deployed in the field, accelerating the path to trusted and resilient digital infrastructure,” said Sami Nassar, SecEdge CEO.
Since September 11, 2026, manufacturers have had to report actively exploited vulnerabilities and severe incidents within 24 hours, with full notification at 72 hours. From December 11, 2027, the Act applies in full: products must ship with a secure default configuration and without known exploitable vulnerabilities, receive free security updates across a support period of five years by default, and pass conformity assessment before CE marking. Meeting those requirements depends on a device being able to prove what it is and protect the keys it holds. SEC-TPM gives OEMs and system integrators a standards-based way to do both, on the processor already in the design and without a board respin.
SEC-TPM is not limited to new designs. It can be added to systems already developed or deployed, as long as the device supports secure firmware update. That gives engineering teams a path to The EU Cyber Resilience Act (CRA) readiness ahead of the December 11, 2027 deadline without a board respin. New designs keep the same security architecture as future i.MX generations arrive, and within Variscite’s pin-compatible families, moving to a higher-performance module does not mean revisiting the security design.
“The CRA does not only apply to whatever our customers are designing now. It applies to everything they already launched and shipped to the market,” said Ofer Austerlitz, VP of Business Development and Sales at Variscite. “SEC-TPM is available across our i.MX-based modules, so implementing it on Variscite products allows our customers to reach TPM 2.0 seamlessly and with no need to redesign their hardware.”